Security Testing and OWASP Top 10
Harry
· 21 Sep 2026
· 1 views
Log in to track your progress and mark lessons complete.
Sponsored
 Browse All Tutorials
Explore →
Introduction to Security Testing
Security testing proves the app resists attackers: authentication, authorisation, input handling, sessions and crypto. Every tester should know the OWASP Top 10.
Core Checks
- Authentication - lockout after retries, no password in URL/logs, secure reset tokens.
- Authorisation - user A cannot fetch user B orders by changing the ID (IDOR); admin APIs reject normal users (403).
- Session - rotate session ID at login, expire on logout, HttpOnly + Secure cookies.
Injection Attacks
- SQL injection - try admin OR 1=1 -- in login; expect rejection, never a dump.
- XSS - submit <script>alert(1)</script> in comments; it must render as text, never execute.
- CSRF - state-changing requests must need anti-CSRF tokens, not just cookies.
OWASP Top 10 (2021) at a Glance
- Broken Access Control, Cryptographic Failures, Injection, Insecure Design.
- Security Misconfiguration, Vulnerable Components, Auth Failures.
- Integrity Failures, Logging/Monitoring Failures, SSRF.
Security Testing Tools
- OWASP ZAP / Burp Suite for proxy scanning and fuzzing.
- Dependency scanners (OWASP Dependency-Check) for known CVEs.
- Browser devtools plus sqlmap for targeted probes.
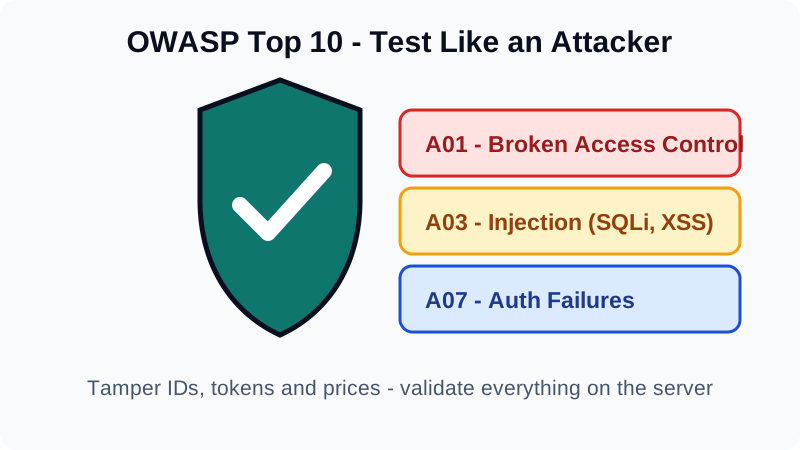
- Deny by default; validate on the server, never only in JS.
- Test with attacker eyes: tamper IDs, tokens and prices.
- Log security events so attacks are visible.